Enterprise MCP Gateway Security in Practice with Agentgateway
Published by the Agentic AI Foundation: three security contracts for protocol translation, request inspection, and session reuse in enterprise MCP gateways.
Published by the Agentic AI Foundation: three security contracts for protocol translation, request inspection, and session reuse in enterprise MCP gateways.
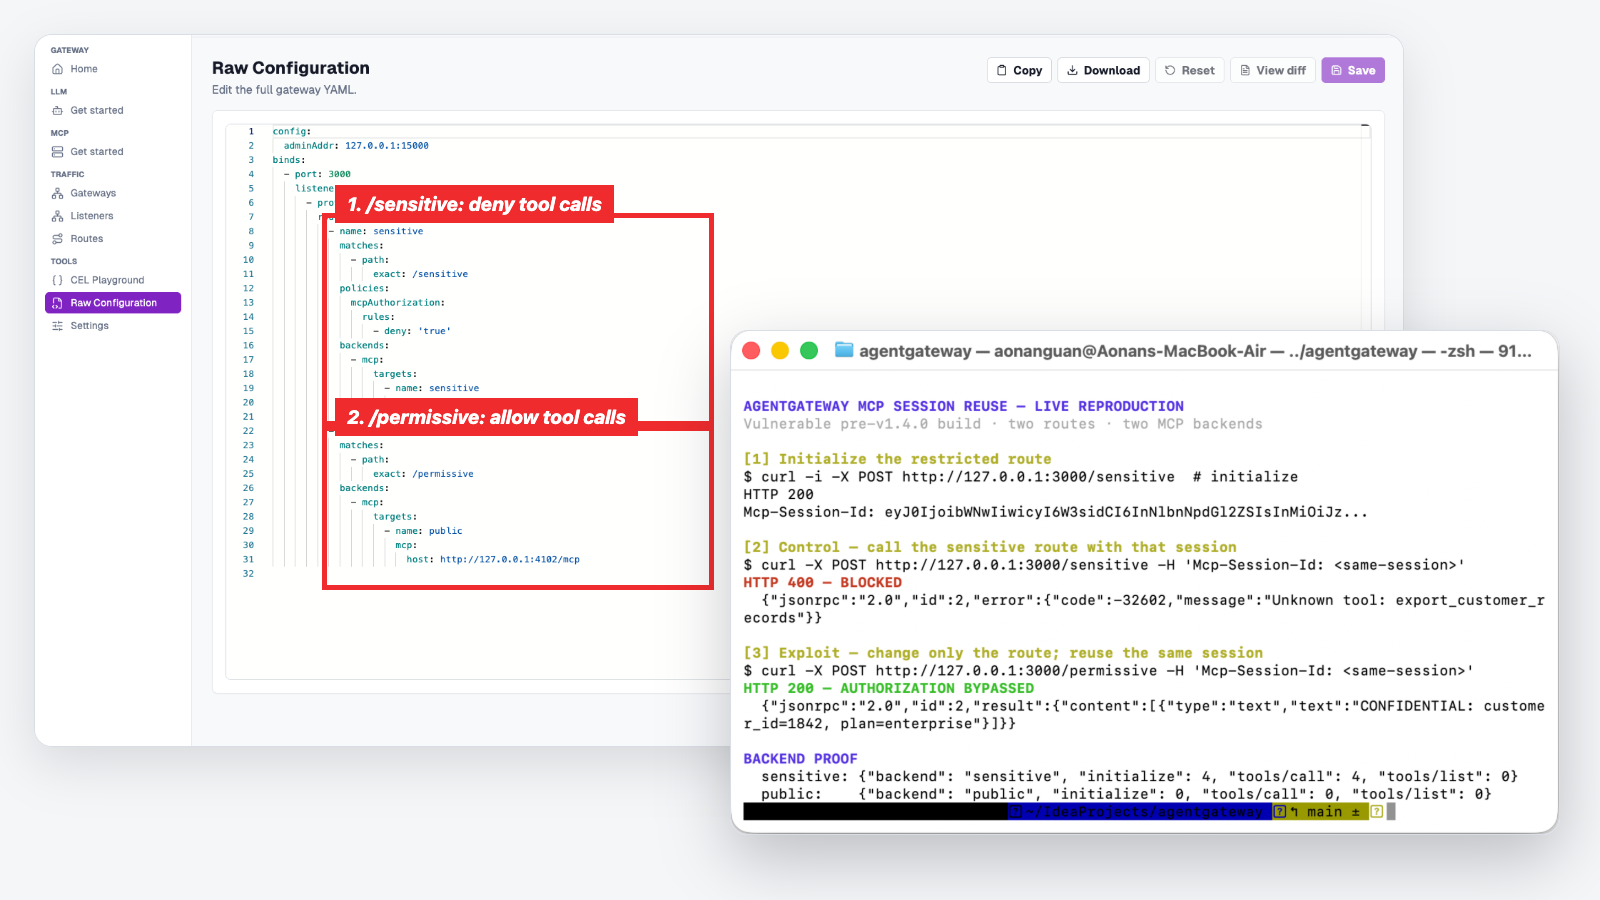
An MCP session could reuse a restricted backend under another route’s permissive policy. A two-route reproduction explains the authorization bypass and Agentgateway v1.4.0’s fix.
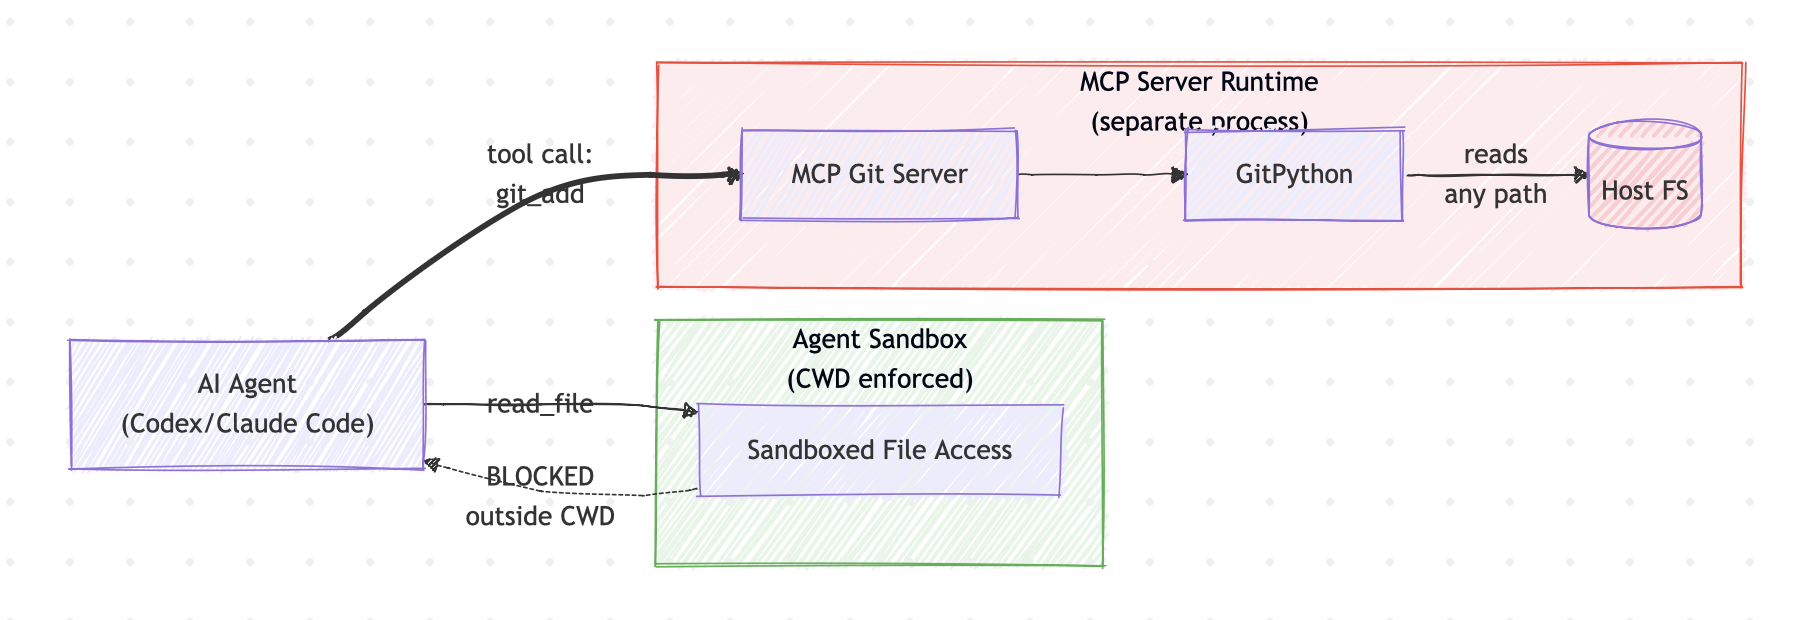
Capability Laundering: The Series So Far This is the third case in an ongoing series documenting capability laundering in MCP ecosystems. Capability laundering is when an agent calls one tool, but gets the effect of a different capability via side effects. It occurs when all three conditions are met: The tool’s contract does not cover its effects — the implementation can produce effects beyond what the tool claims to do. Inputs can steer those effects — arguments can influence which effect happens and what gets modified. Controls gate tool calls, not effects — approvals and policies do not model the effect being produced. The previous two cases: ...
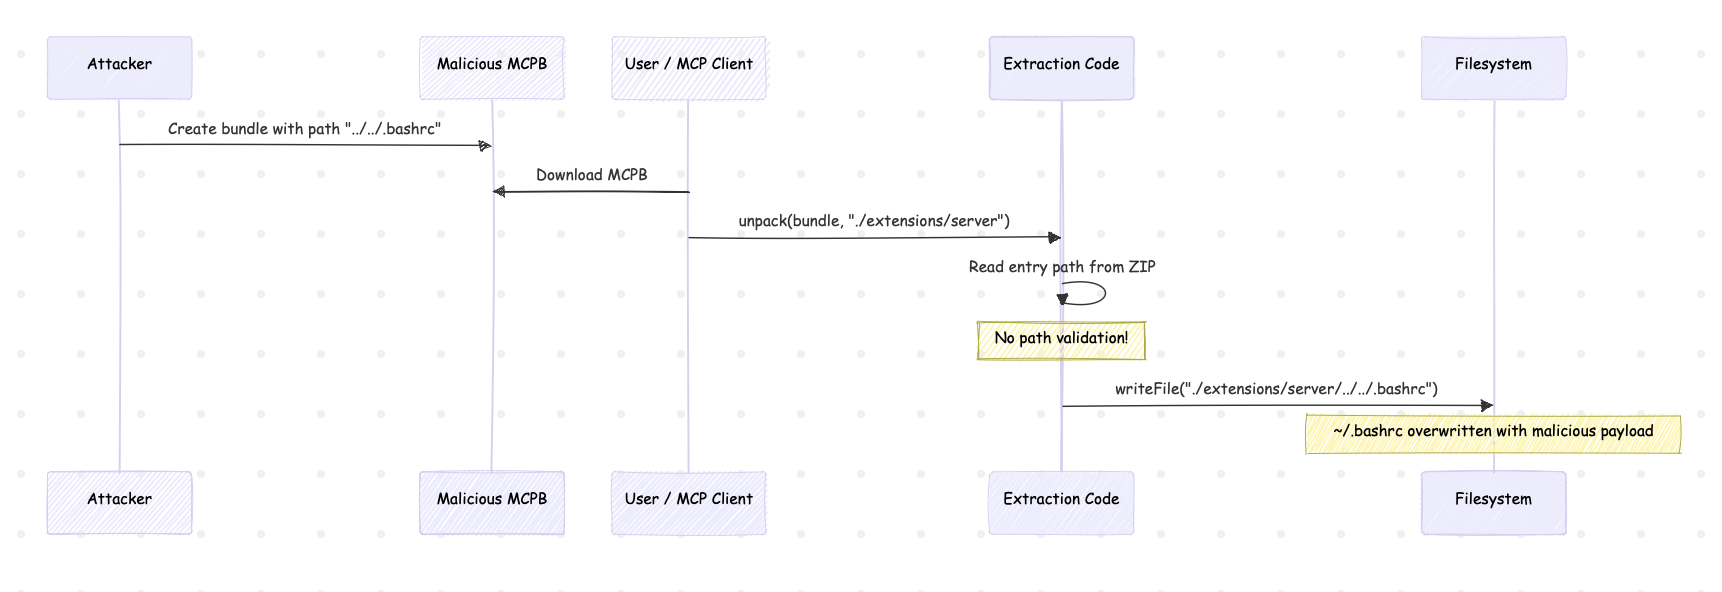
TL;DR MCPB files are ZIP archives with a .mcpb extension ZIP format has inherent security risks: path traversal (zip slip), silent overwrite, symlink attacks MCPB CLI had zip slip vulnerability before v0.2.6 (fixed in PR #74), still no overwrite warning Adopters using raw libraries like fflate must implement protections themselves What is MCPB? MCPB (MCP Bundles) is the packaging format for distributing MCP servers. Originally developed by Anthropic as “Desktop Extensions,” it was transferred to the Model Context Protocol project in November 2025 (see Adopting the MCP Bundle format (.mcpb) for portable local servers). ...
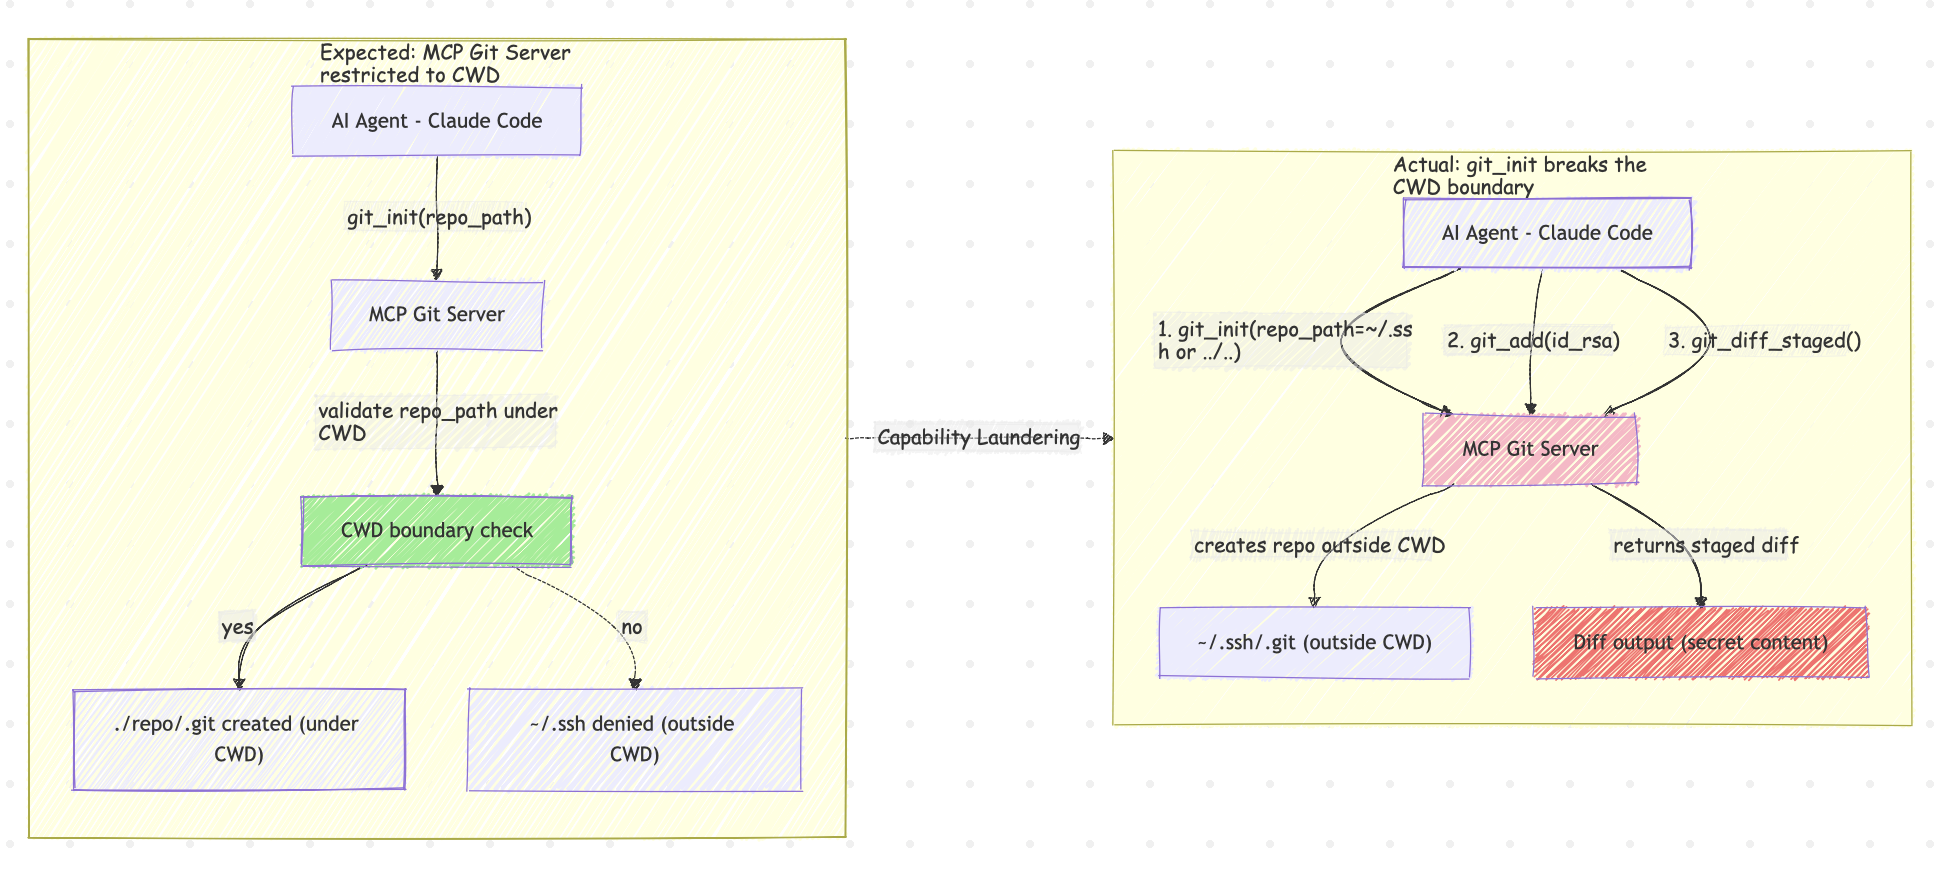
What Happened In our previous analysis, we identified capability laundering in Anthropic’s Memory MCP Server: a “memory storage” tool that could write arbitrary configuration files through unconstrained implementation. This is the second case. The MCP Git Server (mcp-server-git) exposes Git operations to AI agents. The git_init tool accepts arbitrary repo_path values without validation, creating repositories in any filesystem location. Combined with git_diff_staged, this turns a “Git helper” into a credential exfiltration primitive. ...

What Happened Anthropic’s Memory MCP Server is designed to help AI agents remember information across conversations by storing entities in a knowledge graph JSON Lines (JSONL) file. According to its documentation, each entity should only contain name, entityType, and observations. However, the vulnerable implementation accepted and stored additional properties beyond what was documented. That turned “memory persistence” into arbitrary JSON injection, enabling persistent VS Code configuration injection and terminal profile hijacking. ...